IT Service Management
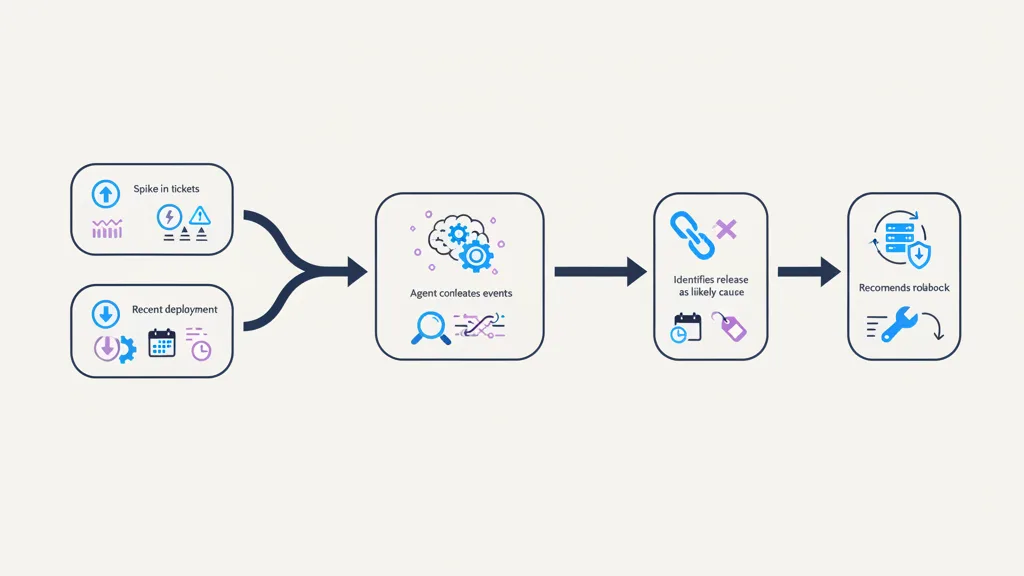
IT Incident Correlation & Root Cause Analysis
Correlates monitoring alerts, incidents, changes and infrastructure data; proposes likely root cause and remediation.
View ApplicationIT Service Management · App Design
Reads change requests, CMDB, previous failures, dependencies and incidents to score risk and coordinate approvals.
Built for: CIO/CTO
End-to-end workflow
Stages retain the source reference workflow. Actor assignments and approval controls are not inferred; deployment responsibilities require review with your process owners.
Change request submitted
agent evaluates affected services + past incidents
assigns risk
gathers approvals
schedules low-risk change
Data sources used in the reference workflow. Integration approach, authentication and permitted actions are assessed for each deployment.
Measures to baseline before a pilot and track afterwards. Fynite does not publish projected results for this application.
Deployment-planning guidance, not a verified configuration for this application. Specific controls require confirmation during evaluation.
Questions
Reads change requests, CMDB, previous failures, dependencies and incidents to score risk and coordinate approvals. In the reference scenario: Change request submitted → agent evaluates affected services + past incidents → assigns risk → gathers approvals → schedules low-risk change.
Have another question? Use the assistant in the corner of this page — it knows this application's details.
Related applications
IT Service Management
Correlates monitoring alerts, incidents, changes and infrastructure data; proposes likely root cause and remediation.
View Application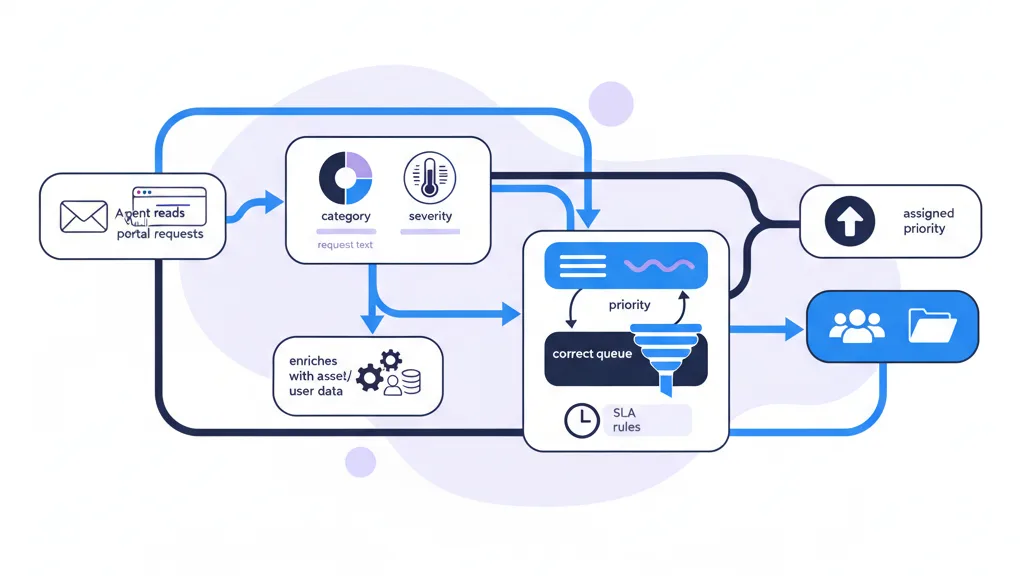
IT Service Management
Classifies, prioritizes and routes tickets using request text, user context and SLA rules.
View Application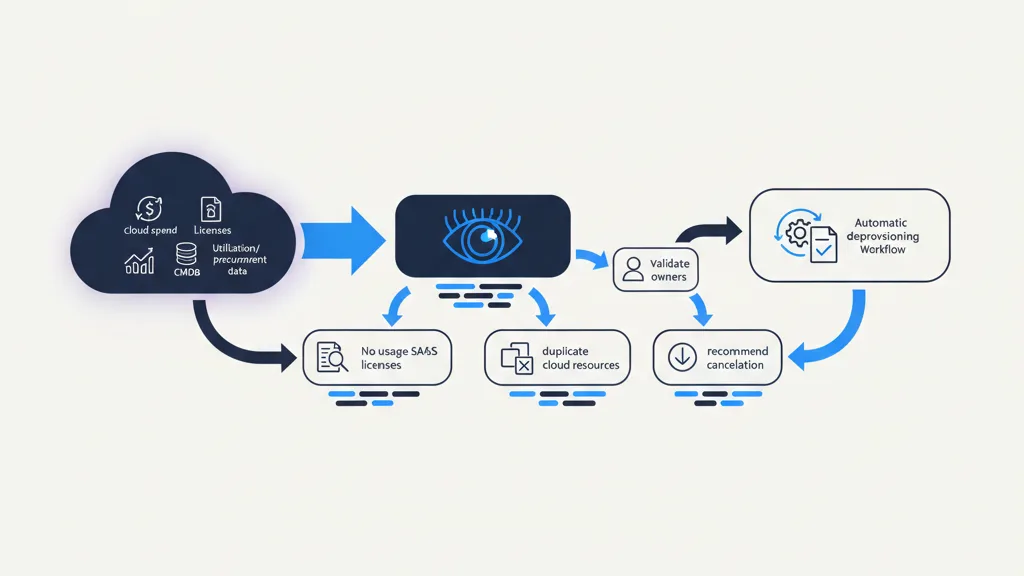
IT Service Management
Combines cloud spend, licenses, CMDB, utilization and procurement data; detects anomalies and executes approved optimizations.
View ApplicationIllustrative evaluation context, not a revised source workflow or verified deployment specification.
Related illustrative examples—not proof that this design implements the workflow or has validated connectors.
Conflicting asset feeds obscure identity, IT/OT classification and service dependencies—making risk prioritization and CMDB changes harder to trust.
Explore This Agent Workflow : OT/IT Asset IntelligenceStart with the outcome
Start from an existing enterprise application or bring your own requirements. See how Fynite can connect your systems, deploy reasoning agents, and turn complex work into governed execution.