IT & OperationsApp Design
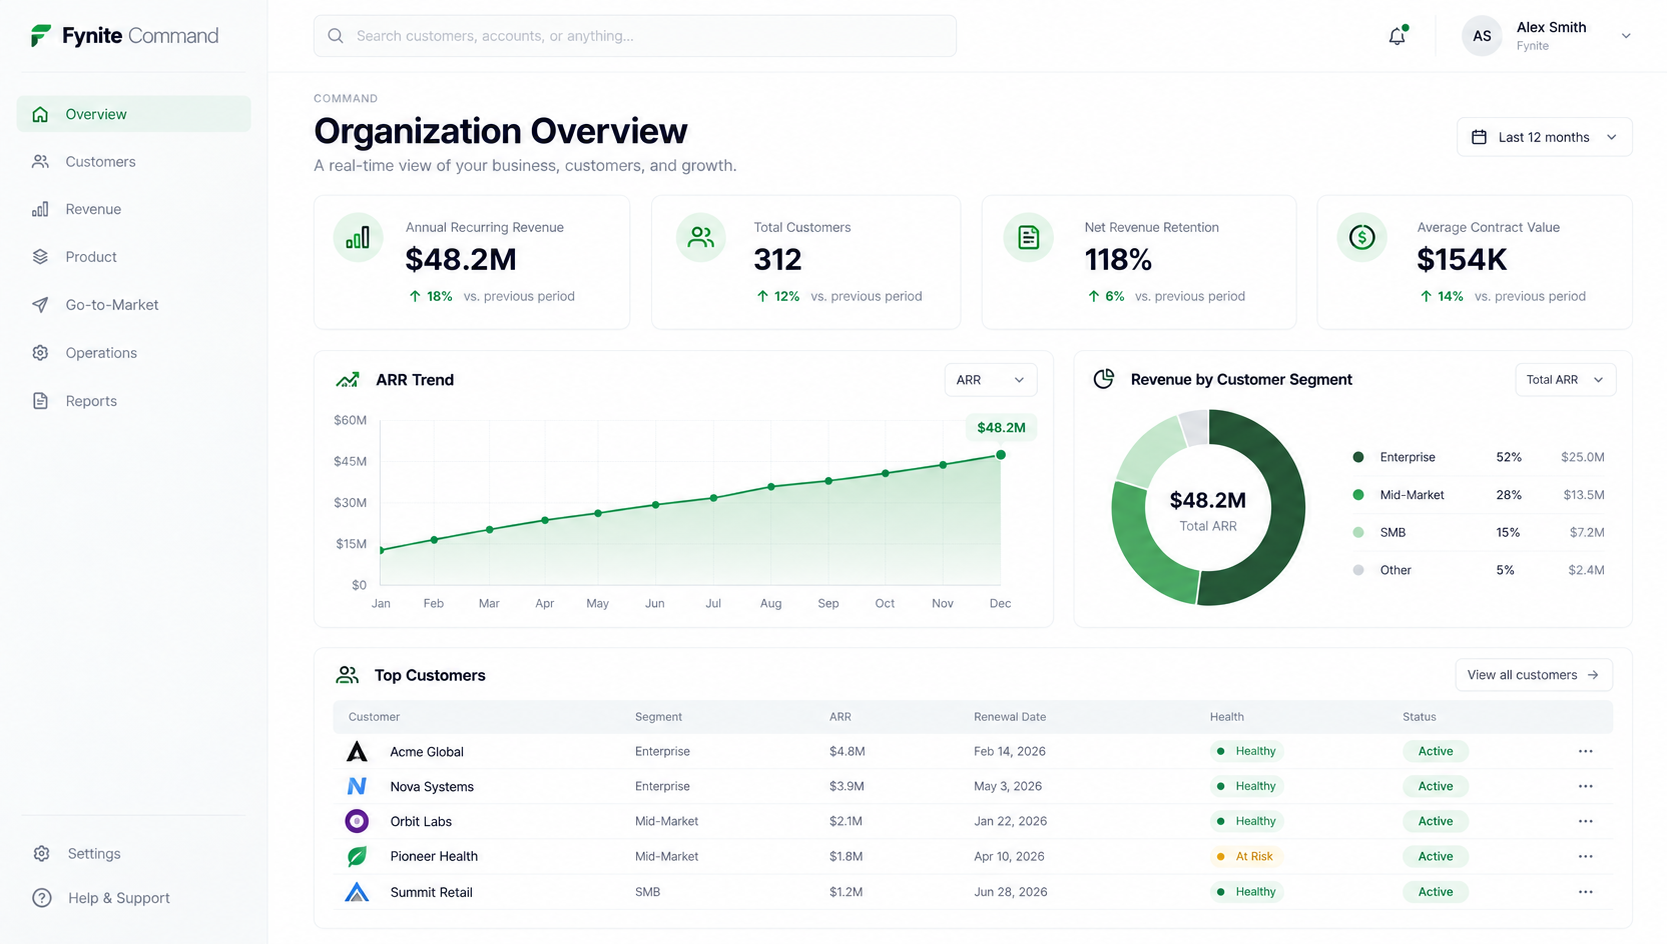
Fynite Command
A company-wide view of customers, revenue, and account health.
Revenue overview ·Customer health ·Operational follow-through ·
View Application IT & Operations / Risk & Compliance · App Design
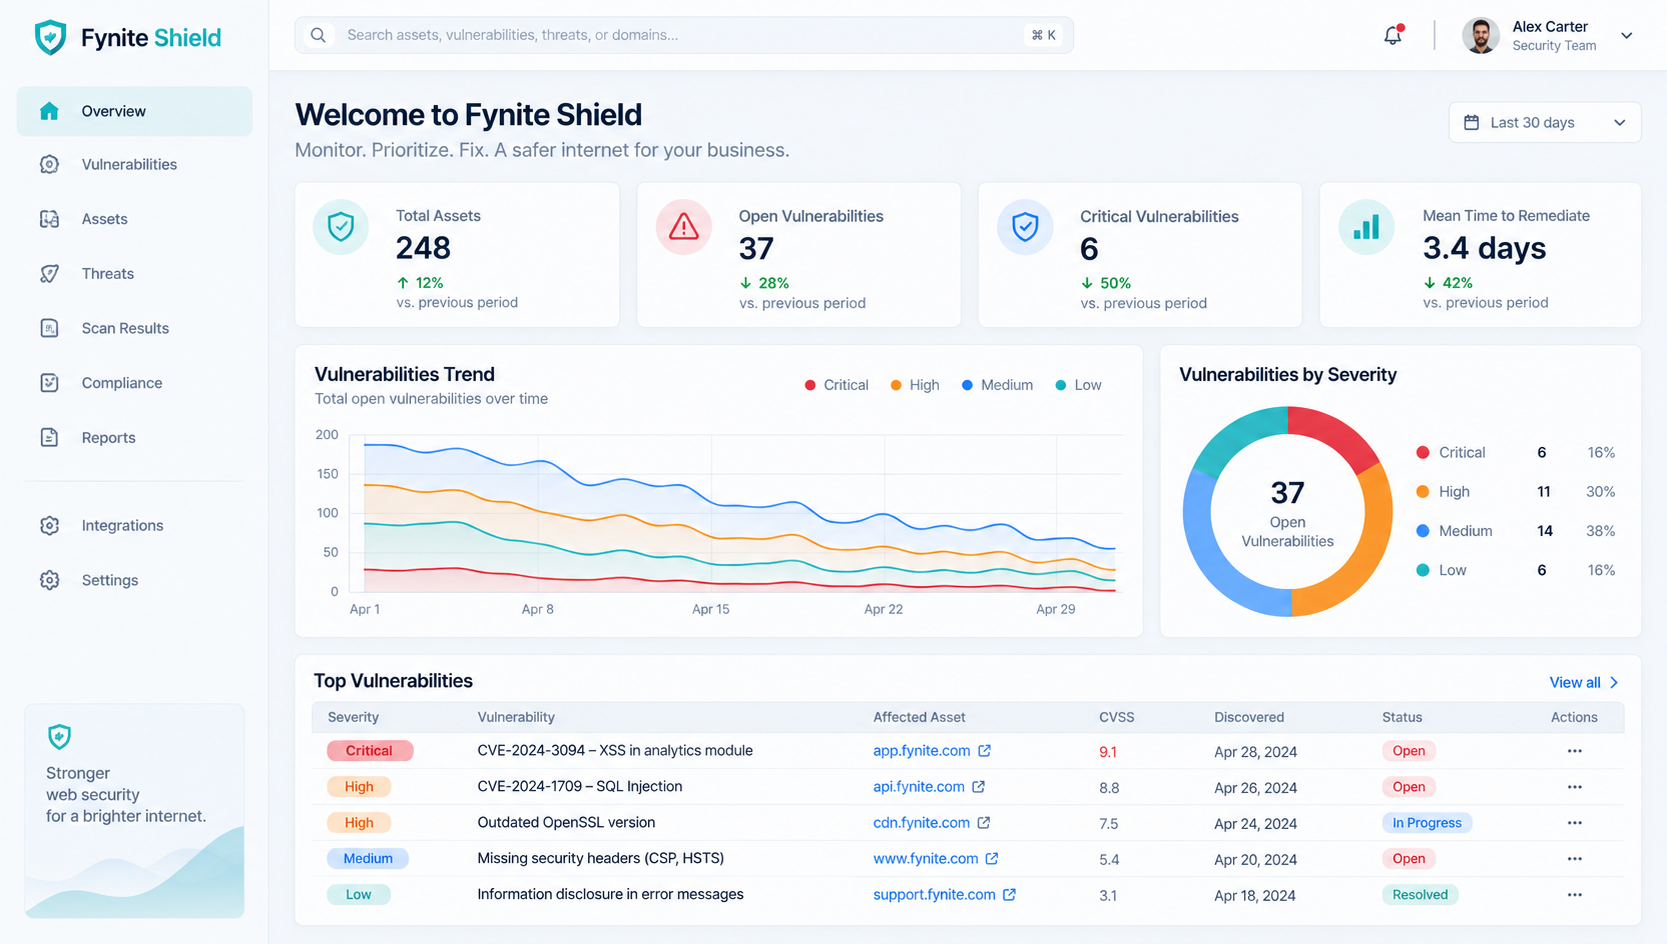
Prioritize vulnerabilities and track remediation across assets.
Business problem
Give security teams one place to see vulnerable assets, prioritize findings, and follow remediation through to resolution.
Designed for security and it teams.
Bring affected assets and findings together.
Separate critical work from lower-severity findings.
Keep owners and resolution status visible.
Operational outcomes
Bring context together, reduce repetitive coordination, and make review ownership visible. Establish a baseline before measuring actual benefits.
Investigate exceptions in shield operations using permitted evidence, then request review before consequential actions.
No specific connector is verified for this design. Confirm source systems, interface availability, credential scope and approved read/write actions during discovery.
Define roles, data boundaries, policy checks and approval thresholds. Review model controls, audit history and deployment requirements before production.
Configuration
Validate ordinary cases, incomplete data and exception paths. Agree deployment and operating ownership; no universal launch timeline is assumed.
Common questions
This is an App Design. Confirm packaged availability and the supported implementation pathway with Fynite before planning a deployment.
Related applications
A company-wide view of customers, revenue, and account health.
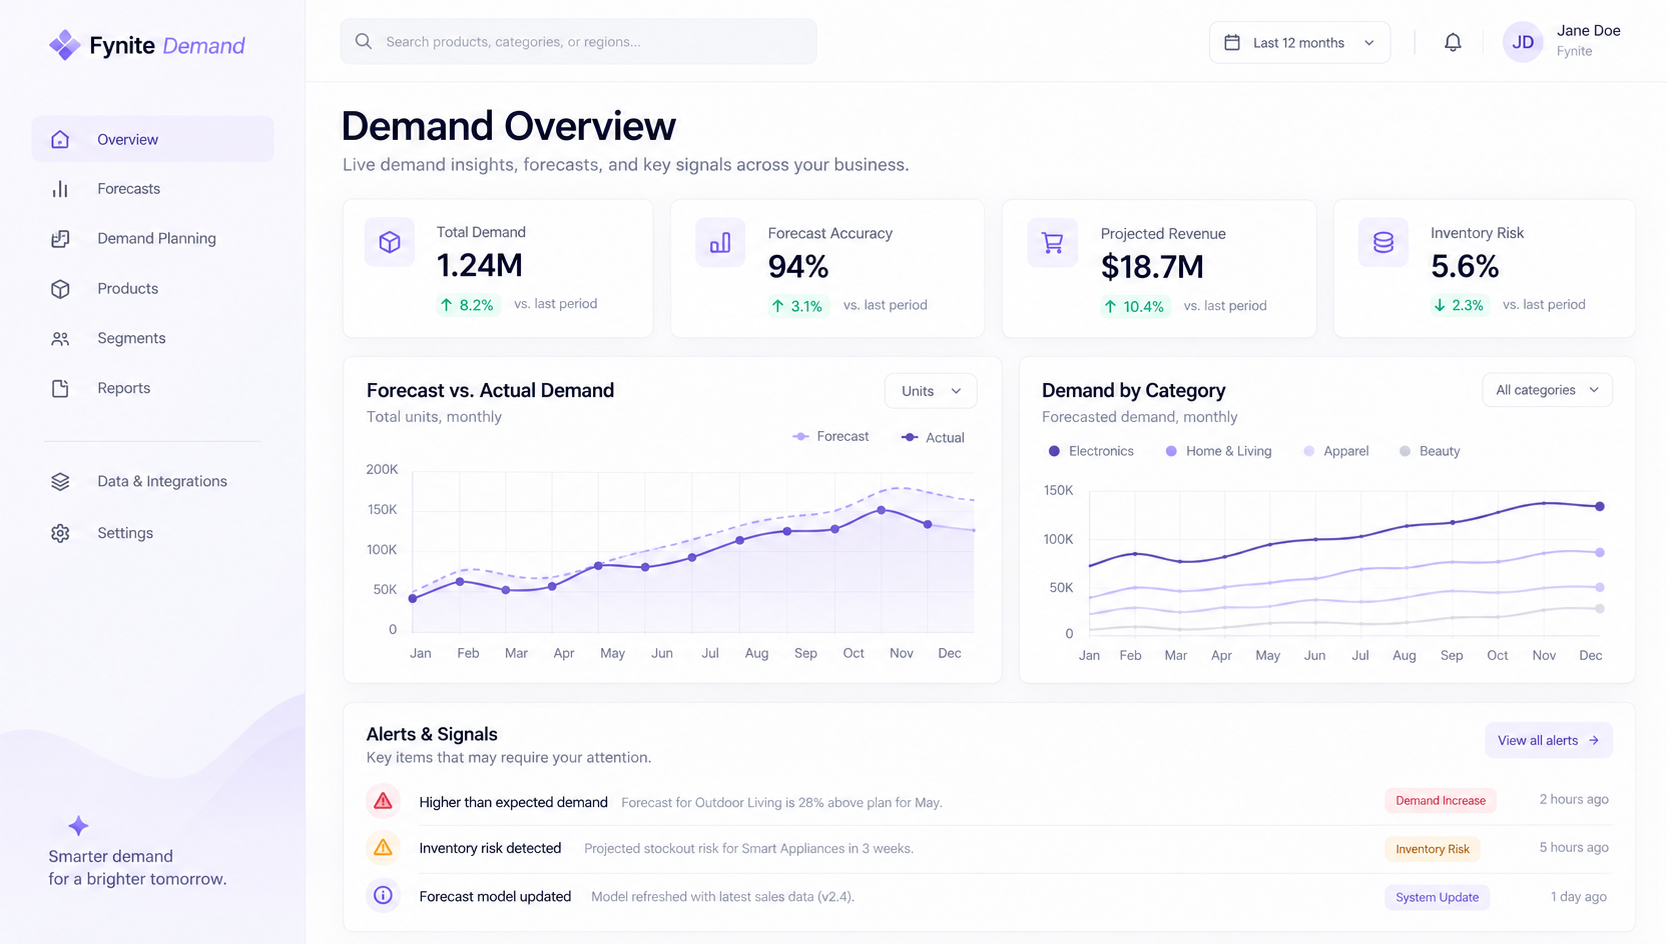
See forecasts, actual demand, and emerging inventory risks together.
Start with the outcome
Start from an existing enterprise application or bring your own requirements. See how Fynite can connect your systems, deploy reasoning agents, and turn complex work into governed execution.