Cybersecurity
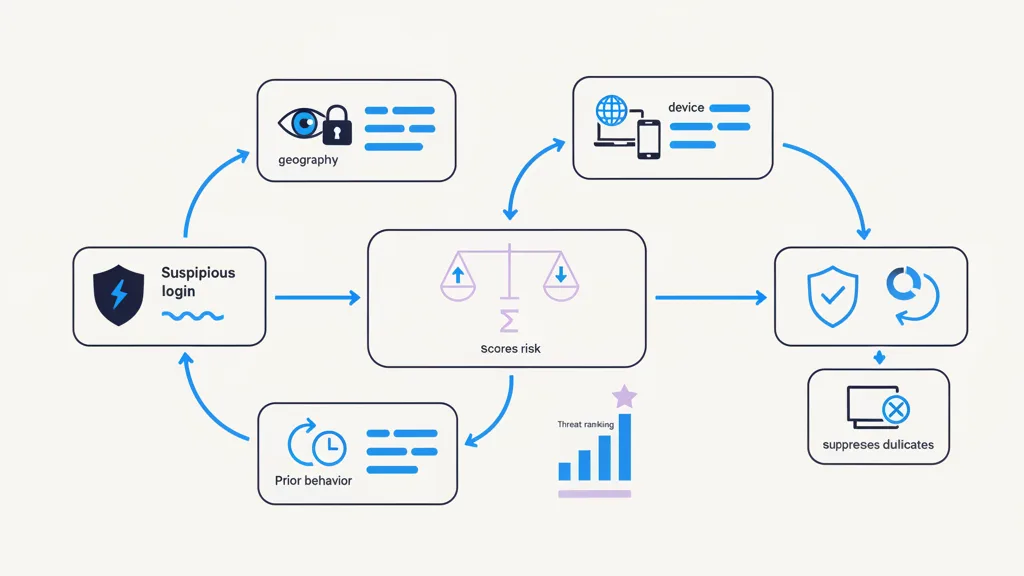
Security Threat Detection, Enrichment & Triage
Combines security alerts, identity, endpoint and asset context; ranks threats and suppresses duplicates.
View ApplicationCybersecurity · App Design
Analyzes reported email, URLs, sender behavior and identity data; quarantines malicious mail and initiates response.
Built for: CISO
End-to-end workflow
Stages retain the source reference workflow. Actor assignments and approval controls are not inferred; deployment responsibilities require review with your process owners.
User reports phishing
agent examines message
searches tenant for copies
quarantines all matches
blocks sender
alerts affected users
Data sources used in the reference workflow. Integration approach, authentication and permitted actions are assessed for each deployment.
Measures to baseline before a pilot and track afterwards. Fynite does not publish projected results for this application.
Deployment-planning guidance, not a verified configuration for this application. Specific controls require confirmation during evaluation.
Questions
Analyzes reported email, URLs, sender behavior and identity data; quarantines malicious mail and initiates response. In the reference scenario: User reports phishing → agent examines message → searches tenant for copies → quarantines all matches → blocks sender → alerts affected users.
Have another question? Use the assistant in the corner of this page — it knows this application's details.
Related applications
Cybersecurity
Combines security alerts, identity, endpoint and asset context; ranks threats and suppresses duplicates.
View Application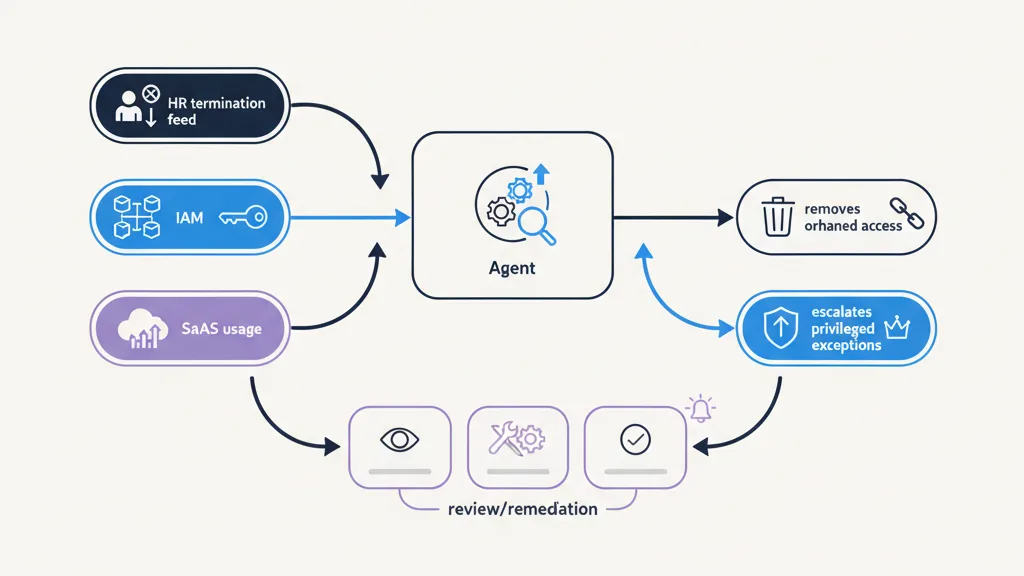
Cybersecurity
Detects anomalous privileges, dormant accounts and access-policy violations; triggers review/remediation.
View Application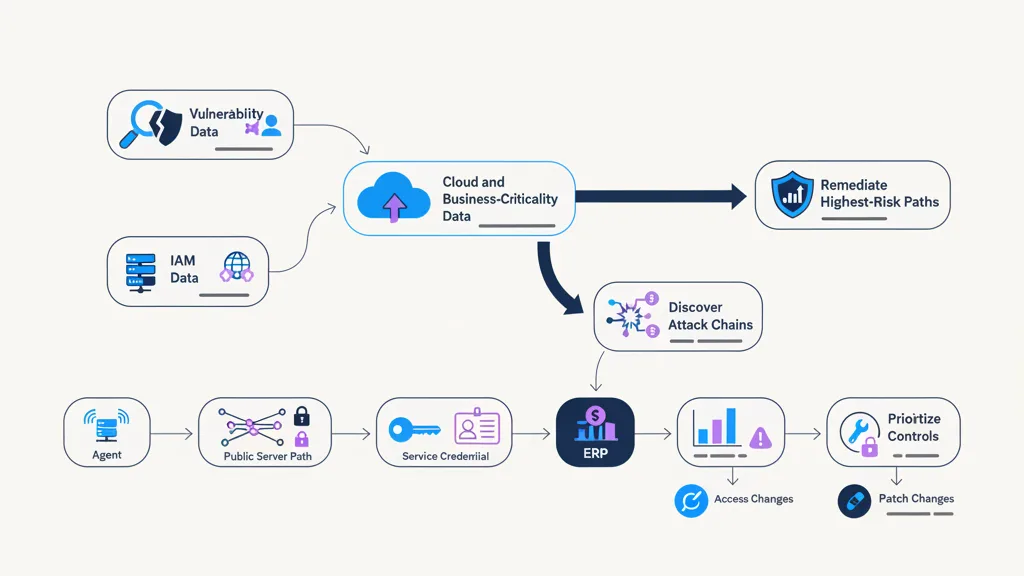
Cybersecurity
Connects vulnerability, IAM, CMDB, cloud and business-criticality data to discover attack chains and remediate highest-risk paths.
View ApplicationStart with the outcome
Start from an existing enterprise application or bring your own requirements. See how Fynite can connect your systems, deploy reasoning agents, and turn complex work into governed execution.