Cybersecurity
Cybersecurity Incident Investigation & Forensic Analysis
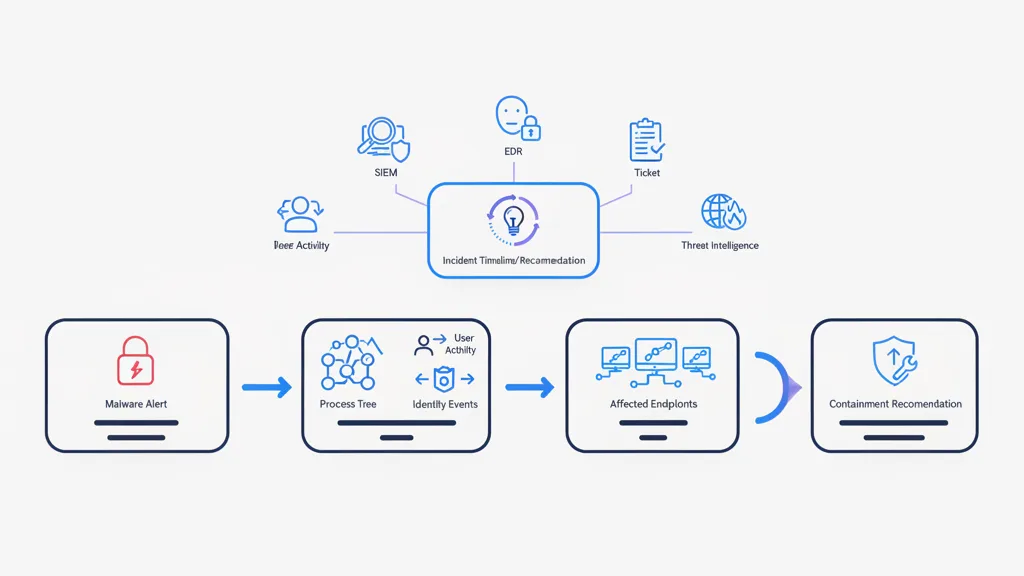
Correlates SIEM, EDR, identity, ticket and threat-intelligence data and builds incident timeline/recommendation.
View ApplicationCybersecurity · App Design
Multi-agent orchestration handles alert enrichment, investigation, containment and documentation with policy guardrails.
Built for: CISO
End-to-end workflow
Stages come from the reference scenario for this application. Each is tagged by who performs it: agent reasoning, governed automation, or human control.
Credential compromise
Governed automation
Agent validates attack
Governed automation
Revokes sessions
Governed automation
Isolates endpoint
Governed automation
Rotates credentials
Governed automation
Updates SIEM/case
Governed automation
Initiates forensic workflow
Governed automation
Data sources used in the reference workflow. Integration approach, authentication and permitted actions are assessed for each deployment.
Measures to baseline before a pilot and track afterwards. Fynite does not publish projected results for this application.
Specific platform controls are confirmed against Fynite's security documentation during evaluation.
Questions
Multi-agent orchestration handles alert enrichment, investigation, containment and documentation with policy guardrails. In the reference scenario: Credential compromise → agent validates attack → revokes sessions → isolates endpoint → rotates credentials → updates SIEM/case → initiates forensic workflow.
Have another question? Use the assistant in the corner of this page — it knows this application's details.
Related applications
Cybersecurity
Correlates SIEM, EDR, identity, ticket and threat-intelligence data and builds incident timeline/recommendation.
View Application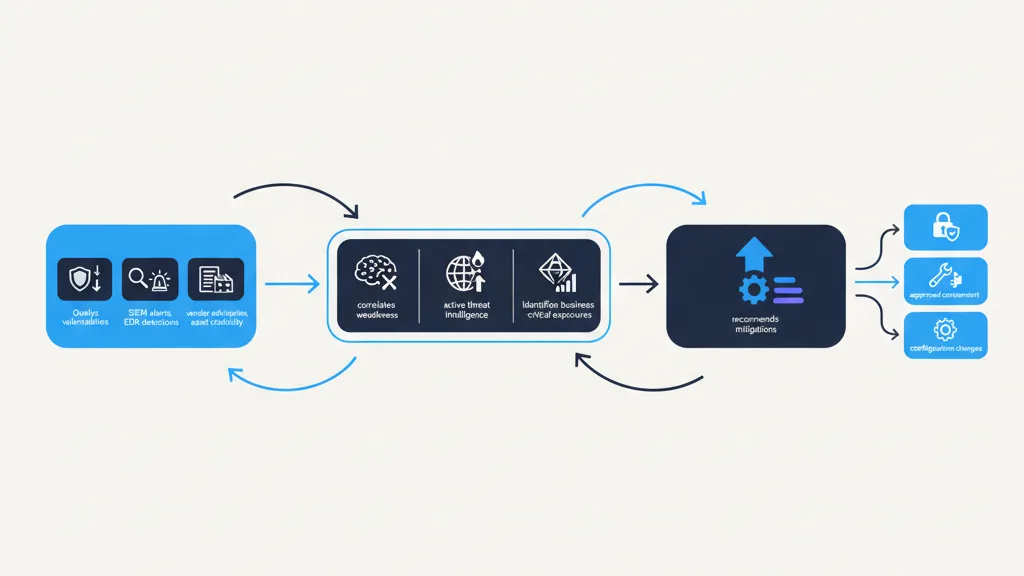
Cybersecurity
Aggregate Qualys, vendor, and internal data into an AI-driven threat management system; assess and remediate risks in real time across infrastructure.
View Application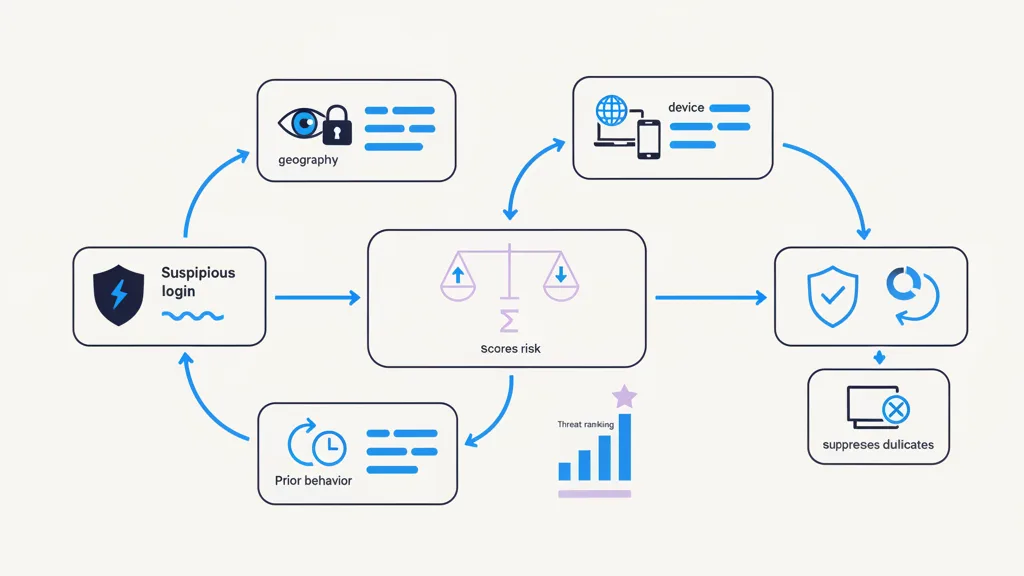
Cybersecurity
Combines security alerts, identity, endpoint and asset context; ranks threats and suppresses duplicates.
View ApplicationStart with the outcome
Start from an existing enterprise application or bring your own requirements. See how Fynite can connect your systems, deploy reasoning agents, and turn complex work into governed execution.